-
 Shankar Jayaraman
- 23 Sep, 2026
Security Questionnaire Fatigue: Why SaaS Teams Need a Better Way to Prove Trust
How SaaS teams can eliminate security questionnaire fatigue by moving from manual spreadsheets to trust centres, reusable evidence, and continuous compliance.
- Shankar Jayaraman
- 16 Sep, 2026
SOC 2 Continuous Monitoring: Moving from Annual Evidence Sprints to Always-On Control Tracking
How to move SOC 2 Type II from annual evidence sprints to continuous, always-on control monitoring, and cut audit prep from weeks to days.
- Shankar Jayaraman
- 10 Aug, 2026
PCI DSS v4.0 for FinTechs: When Payment Security Becomes an Operational GRC Problem
PCI DSS v4.0 guide for FinTechs: 64 mandatory requirements, continuous evidence collection, MFA, targeted risk analysis, vendor oversight and multi-framework GRC.
- Shankar Jayaraman
- 07 Aug, 2026
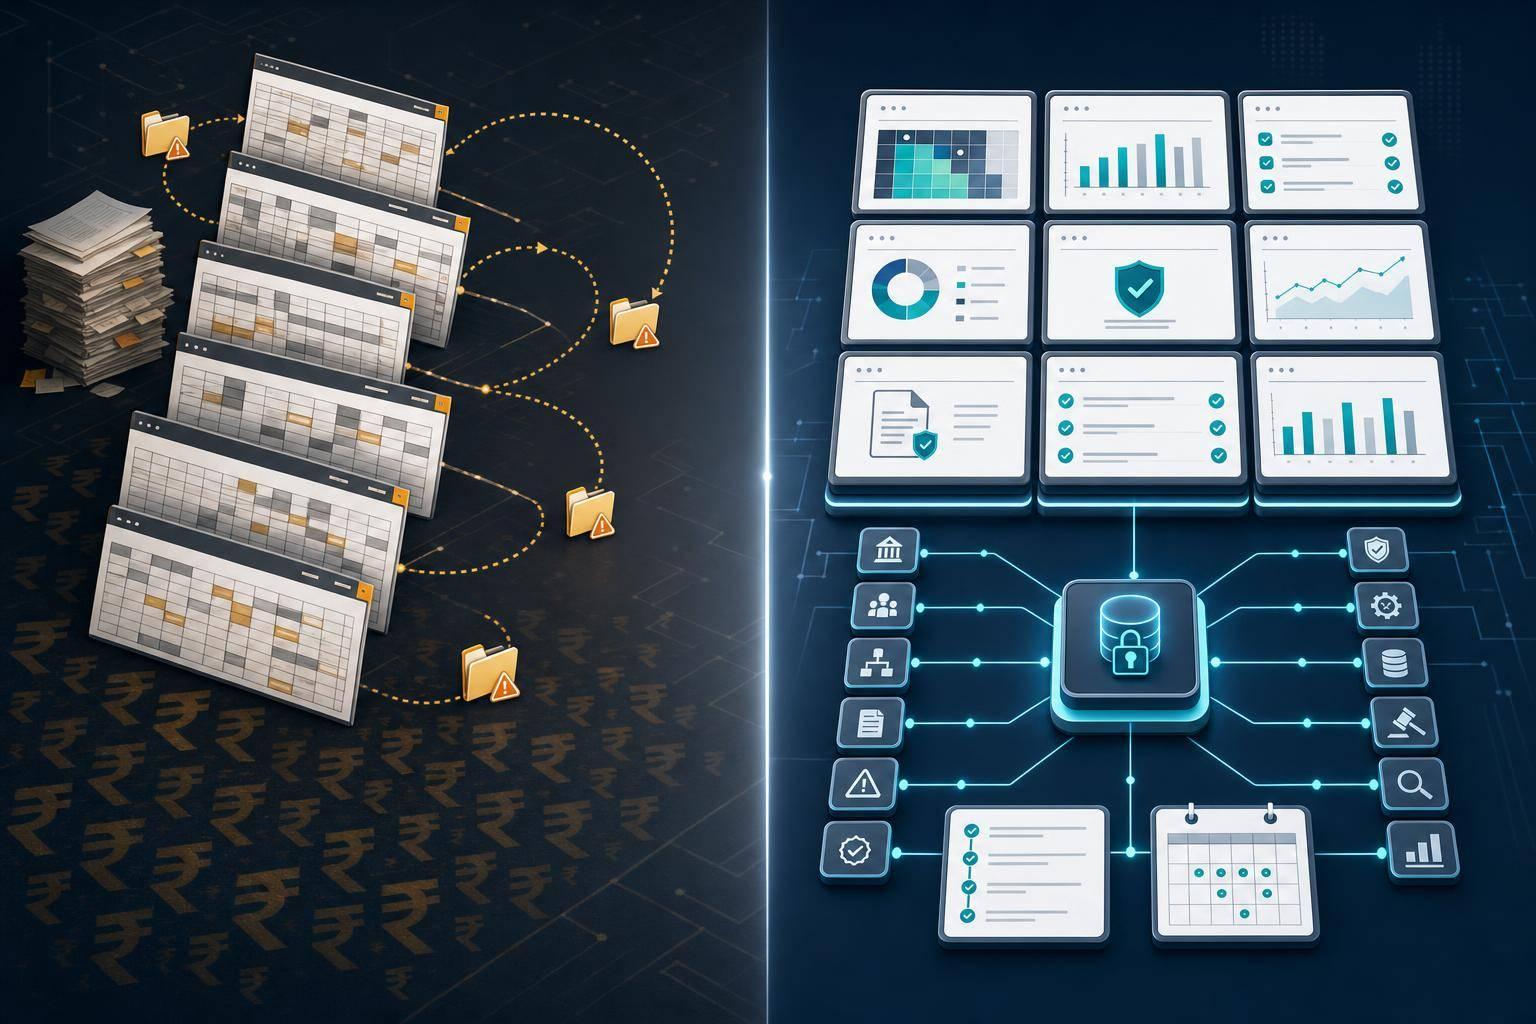
GRC Platform vs Spreadsheet: The Real Cost of Manual Compliance at Scale
How spreadsheets drive hidden compliance costs in India — evidence chasing, version drift and admin overload, and when to move to GRC.
- Shankar Jayaraman
- 07 Aug, 2026
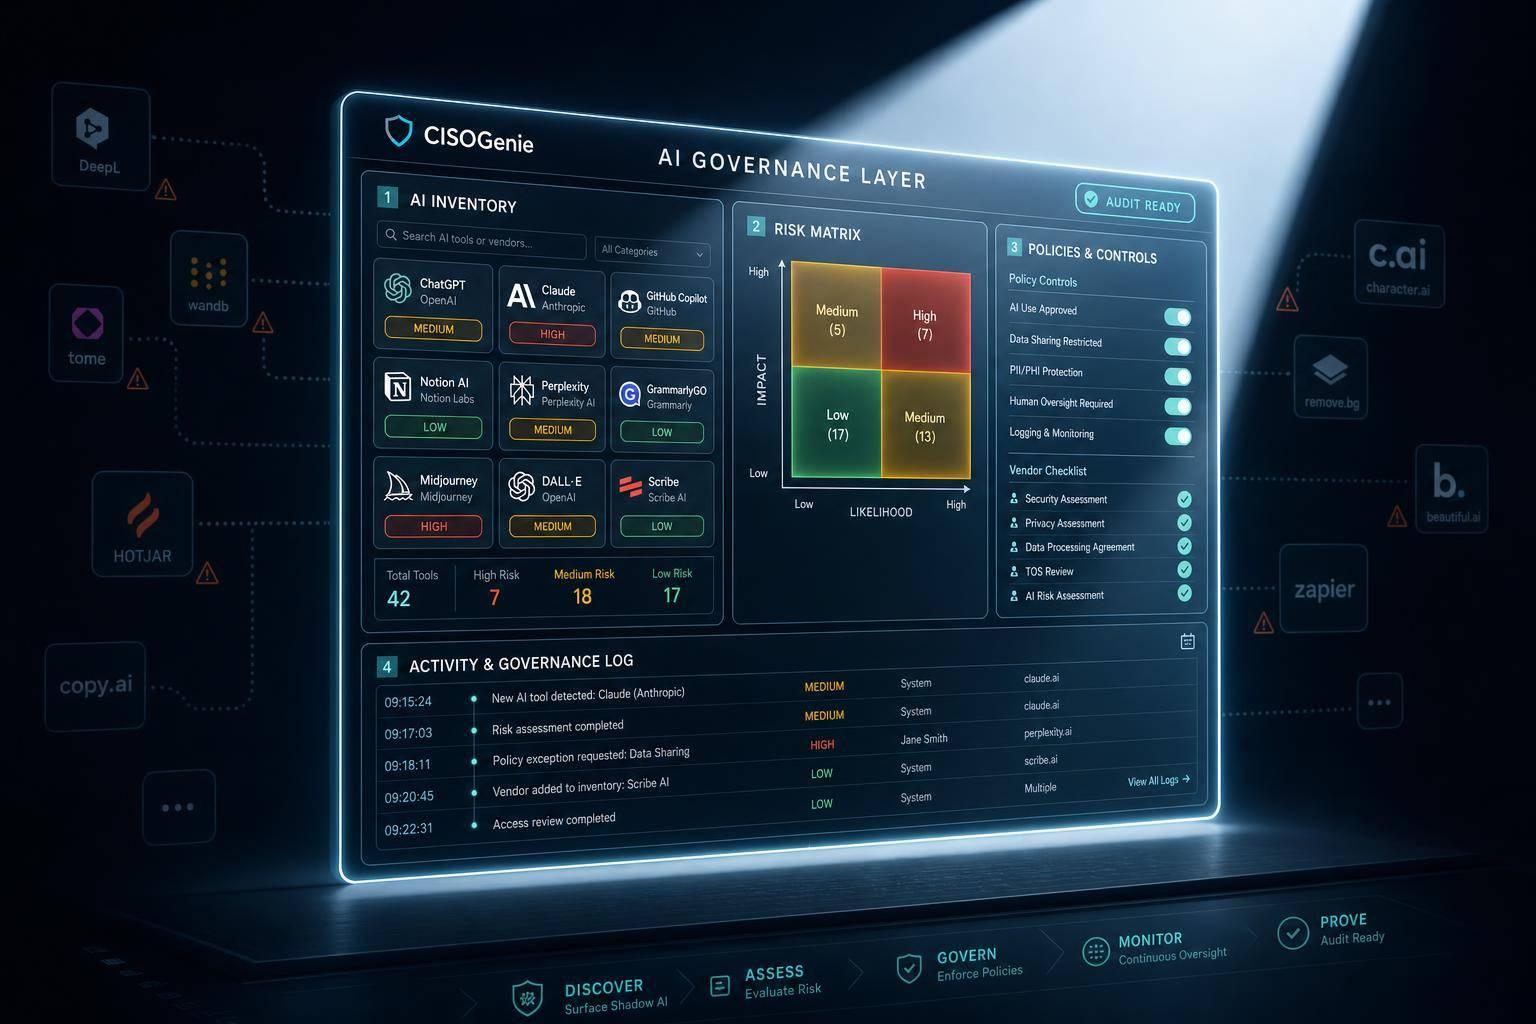
Shadow AI Is Now a Compliance Problem: How to Build an AI Governance Layer Before Your Next Audit
Inventory and risk-rate all AI tools, set policies and vendor checks, and gather logs to make shadow AI audit-ready in 30 days.
- Shankar Jayaraman
- 07 Aug, 2026
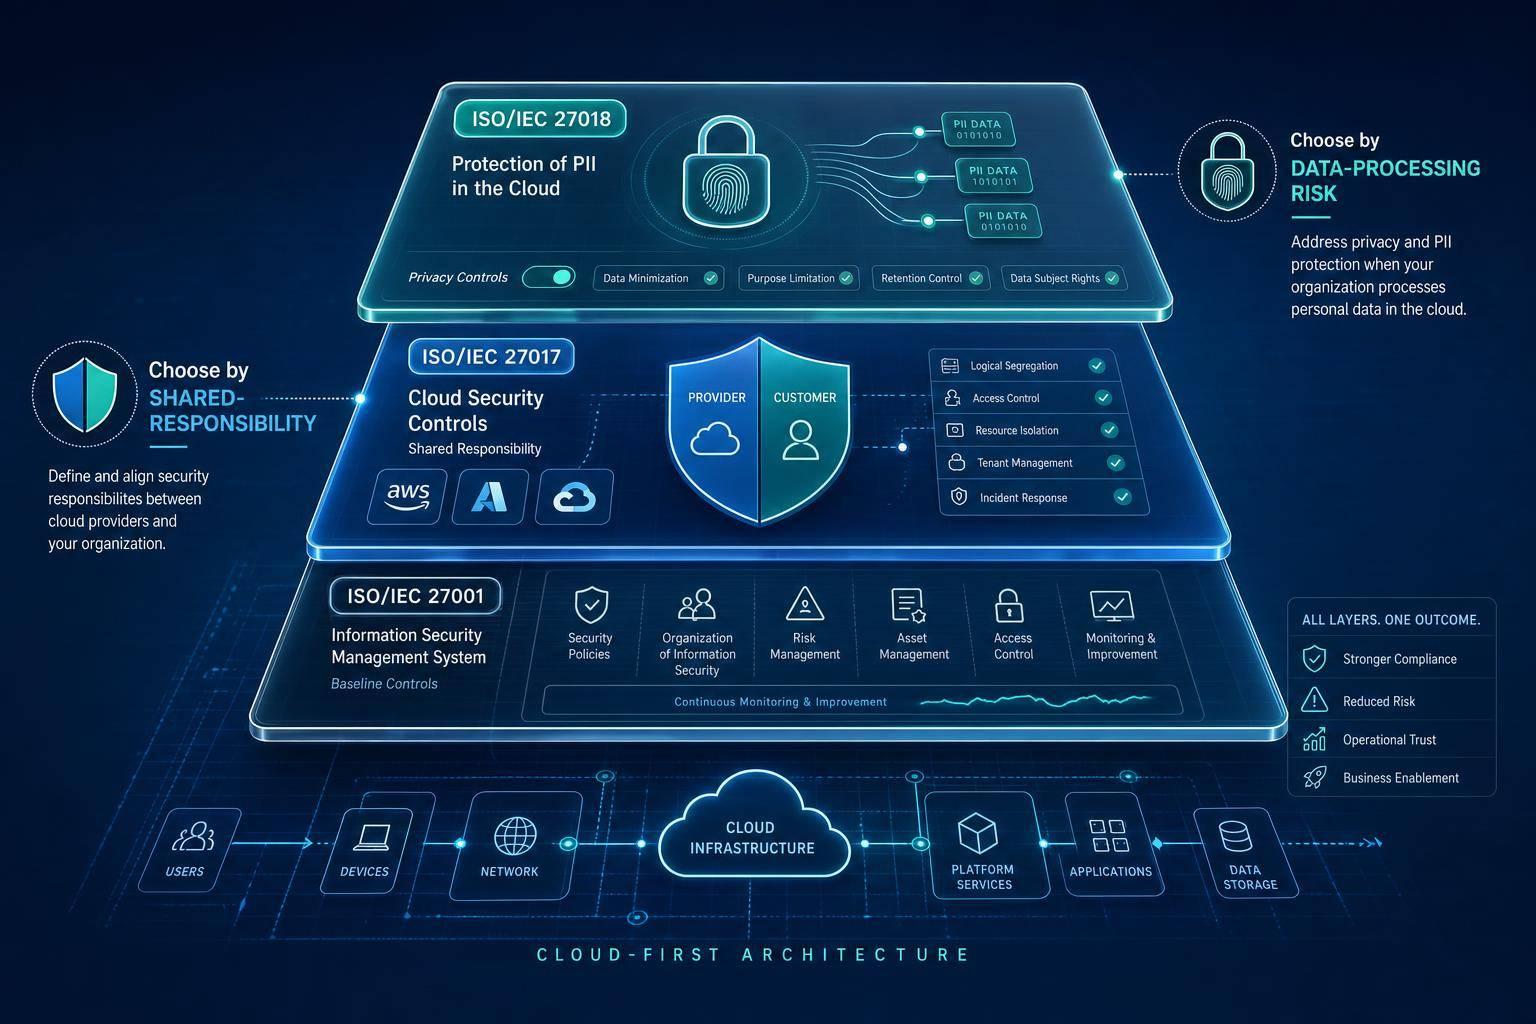
Beyond ISO 27001: A Practical Guide to ISO 27017 and ISO 27018 for Cloud-First Organizations
Extend ISO 27001 with ISO 27017 for cloud gaps and ISO 27018 for PII; choose by shared-responsibility or data-processing risk.